Security Operations (SOC)
Fully managed 24/7 Security Operations Center (SOC) service: continuous threat monitoring, detection, triage and response.
What we deliver
Round-the-clock monitoring, threat detection and incident response delivered by certified security analysts, acting as an extension of your team.
AI-assisted threat hunting and correlation across endpoints, network and cloud. Rapid triage, containment and eradication to minimize dwell time.
Every alert reviewed by human analysts. False positives filtered, real threats escalated with full context, severity rating and recommended action.
SIEM deployment, tuning and management, so your SOC gets log data it can actually act on.
Executive-level reporting on the threat landscape, incident trends, key risks and recommended security improvements, board-ready every month.
When a breach occurs, we contain it fast and investigate thoroughly. Root cause analysis, evidence preservation and recovery coordination from a dedicated response team.
How it works
Every engagement follows the same five steps: baseline the current state, design the target model, roll out in stages, operate it, and improve against measurements.
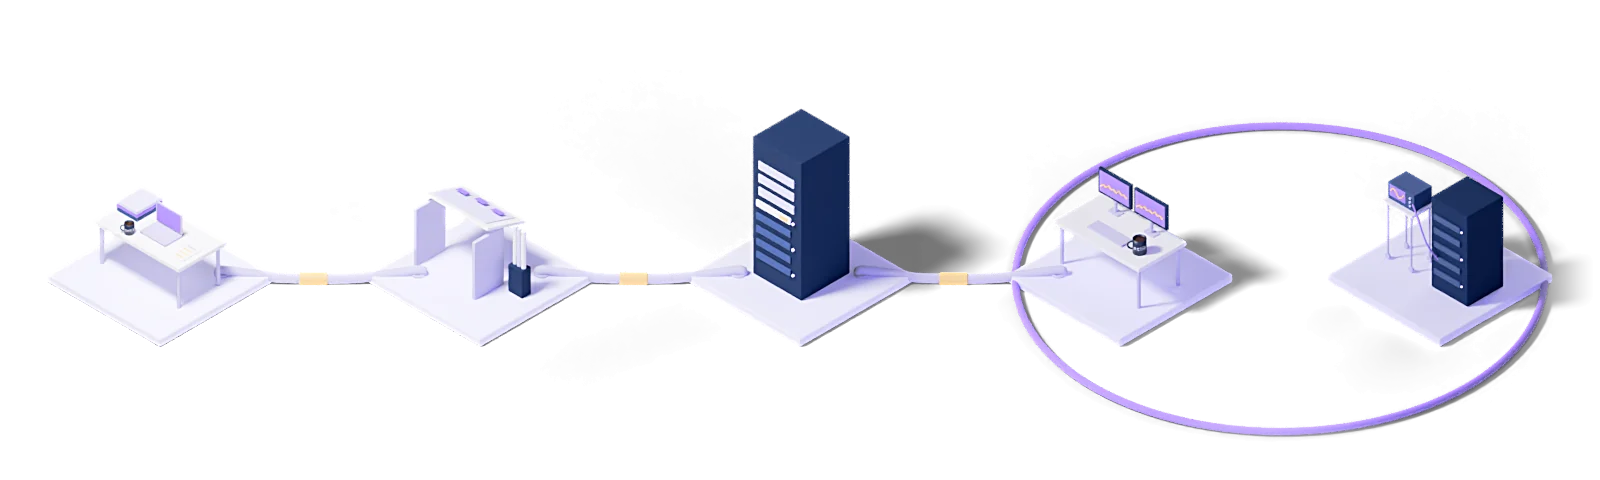
Assess
Baseline the current state, name the gaps and put the success criteria in writing.
Design
Architect the target operating model and the toolchain it needs.
Deploy
Implement, configure and validate in a staged rollout.
Operate
24/7 management with contracted response times and proactive monitoring.
Improve
Continuous improvement driven by metrics, incidents and changes in the business.
Every engagement runs under a written SLA: a commitment, not a best-effort promise.
Dedicated engineers who know your stack. No generalist help-desk tier in between.
Service reviews every two weeks, roadmap updates every quarter.
The concepts behind this service
- Cybersecurity
- Protecting information systems, networks and data against attack.
This section explains the technical terms used on this page. The definitions come from Eclit's own technology glossary, and each term links through to its full entry there.
The full technology glossary →Knowledge Hub
What we have written about running and managing technology, collected in one place.
What Is Cybersecurity? Types, Threats and Core Controls
9 min readWhat Is an Exploit? Zero-Days, Exploit Kits and How to Defend
5 min readPHP2Shell: A 5-Step Checklist for the Critical PHP Vulnerabilities
8 min readWhat Is Phishing? Types, Warning Signs and Defenses
9 min readWhat Is Social Engineering? Attack Types and Defenses
9 min readWhat Is Malware? Types, Trojans and Protection
9 min readWhat Is Ransomware? How Attacks Work and How to Prevent Them
9 min readRansomware Recovery Playbook: Immutable Backups and Journal Rewind
4 min readDoes Türkiye's Cybersecurity Law Apply to You? The 15 Critical Infrastructure Sectors
5 min readLog Retention Periods: Which Records to Keep and for How Long
4 min readWhy a Ransomware Victim Was Fined by Türkiye's KVKK
6 min readHow to Build 72-Hour Data Breach Notification Readiness
7 min readWhat Are SIEM and SOC? How They Differ and Work Together
9 min readWhat Is a Log? Log Records, Log Management and Retention
7 min readWhat Is Endpoint Security? Antivirus, EDR and XDR
7 min readWhat Is Data Poisoning in AI, and How Do You Prevent It?
9 min readWhat Is a Brute Force Attack, and How Do You Prevent It?
10 min read01What does a security operations service cover?
Log collection, correlation, alert triage, first response and incident management. Scope is defined by the list of monitored sources: an attack against a system that is not on the list is not visible.
02How do you reduce false positive volume?
Through rule tuning and learning the environment's own baseline. The first weeks are noisy because what is normal is not yet known; without tuning the team stops reading alerts and the real incident disappears into the noise.
03What happens when an incident is detected?
Validation, prioritization, containment and notification, all following a defined runbook. Who is informed when, and who holds which authority, is written in advance; none of it is debated during the incident.
04How long are logs retained?
The statutory minimum is the baseline, with investigation needs added on top. Short retention is cheap but insufficient to show when an incident began: most attacks start weeks earlier.
05Do you support KVKK data breach notification?
On the technical side, yes: a timeline and evidence pack establishing what was affected, when and to what extent. The notification decision and legal assessment stay with you and your legal advisers.
Let's work out where to start
Within two weeks you get it in writing: what works, what carries risk, and a prioritized roadmap.
Request a conversation