Identity Management
IAM, PAM, SSO and MFA, delivered end to end. Control who accesses what, automate the full user lifecycle and eliminate the identity risks that cause the majority of breaches.
What we deliver
Design, deploy and manage your IAM framework end to end, covering user provisioning, role-based access control, access reviews and lifecycle automation from joiners to leavers.
Protect and control privileged accounts, the highest-risk credentials in your environment. Session recording, just-in-time access and password vaulting for admin and service accounts.
Deploy SSO across your application estate to simplify secure access, and enforce MFA everywhere, eliminating credential-based attack vectors without impacting user experience.
Audit, clean up and manage your AD/Entra ID environment, removing stale accounts, enforcing group policies and ensuring your directory is a trusted, accurate source of identity.
Automate the full user lifecycle, from pre-boarding provisioning through role changes to secure offboarding. Access changes as soon as someone's role or employment status does.
Periodic automated access reviews that flag excess permissions, dormant accounts and policy violations. Maintain a least-privilege posture across your entire user base.
How it works
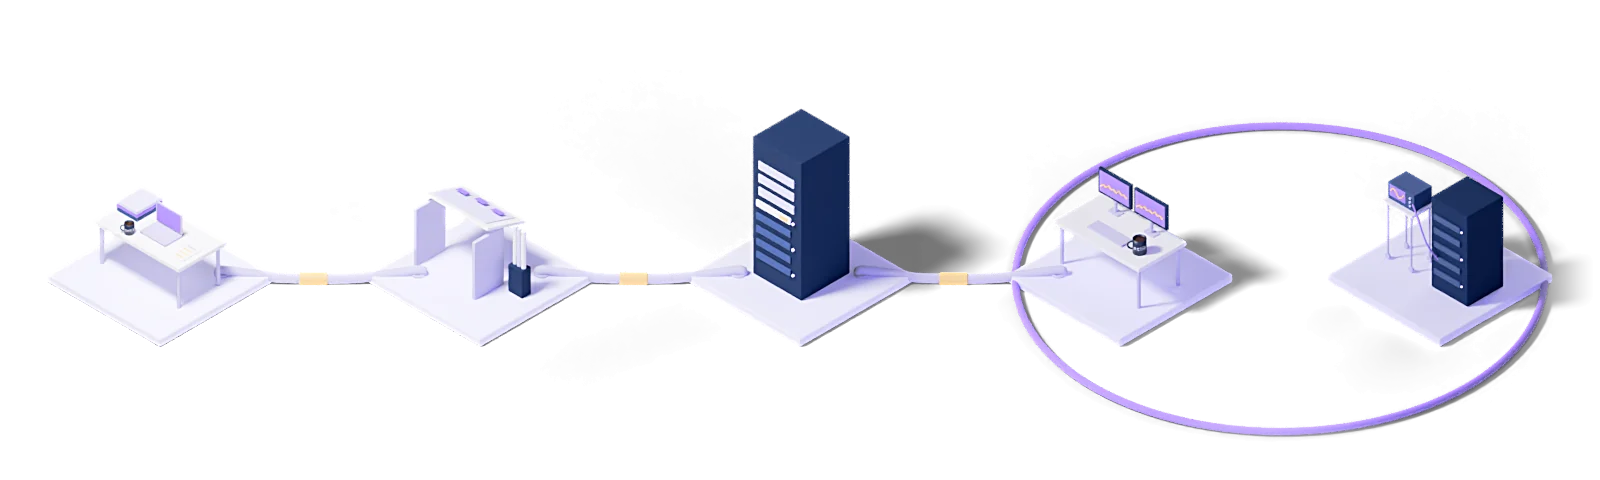
Every engagement follows the same five steps: baseline the current state, design the target model, roll out in stages, operate it, and improve against measurements.
Assess
Baseline the current state, name the gaps and put the success criteria in writing.
Design
Architect the target operating model and the toolchain it needs.
Deploy
Implement, configure and validate in a staged rollout.
Operate
24/7 management with contracted response times and proactive monitoring.
Improve
Continuous improvement driven by metrics, incidents and changes in the business.
Every engagement runs under a written SLA: a commitment, not a best-effort promise.
Dedicated engineers who know your stack. No generalist help-desk tier in between.
Service reviews every two weeks, roadmap updates every quarter.
Who uses this
The industries we run Identity Management for.
The technologies we run this on
The concepts behind this service
- Active Directory
- Microsoft's directory service.
- Zero trust
- A security model in which being inside the network confers no trust.
This section explains the technical terms used on this page. The definitions come from Eclit's own technology glossary, and each term links through to its full entry there.
The full technology glossary →Knowledge Hub
What we have written about running and managing technology, collected in one place.
What Is IAM? Identity and Access Management, PAM and SSO
10 min readWhat Is MFA? Two-Factor and Multi-Factor Authentication
9 min readWhat Is SaaS? Examples, Benefits and SaaS Integration
7 min readHow Long ISO 27001 Certification Actually Takes
5 min readLog Retention Periods: Which Records to Keep and for How Long
4 min readDoes Türkiye's Cybersecurity Law Apply to You? The 15 Critical Infrastructure Sectors
5 min readWhy a Ransomware Victim Was Fined by Türkiye's KVKK
6 min readWhat Is Cybersecurity? Types, Threats and Core Controls
9 min readWhat Is Business Email? Management and Security
9 min readWhat Is Phishing? Types, Warning Signs and Defenses
9 min readWhat Is Social Engineering? Attack Types and Defenses
9 min readWhat Is an AI Agent? Agentic AI and How AI Agents Work
10 min readWhat Is MCP (Model Context Protocol)? Servers and Security
9 min readWhat Is a Brute Force Attack, and How Do You Prevent It?
10 min read01How long does single sign-on take to implement?
It depends on the number of applications and their protocol support. Modern applications supporting SAML or OIDC connect within days; legacy applications may need a broker. A realistic timeline is given once the inventory exists.
02Where should we start with multi-factor authentication?
Administrator accounts and remote access. Those are the two highest-risk surfaces, and the small user count means low resistance. It then rolls out to all users in stages.
03Is SMS-based verification enough?
Better than nothing, but the weakest method: it is exposed to SIM-swap attacks. App-based codes or hardware keys are recommended; hardware keys should be preferred for administrator accounts.
04How quickly is a leaver's access removed?
Within minutes where the identity source is connected to the HR system. Where it is not, the process runs by hand and delay is inevitable: a leaver's account still open is among the most common audit findings.
05How do you manage privileged accounts?
Vaulting, session recording, time-bound elevation and regular password rotation. Temporary privileges granted when needed replace standing administrator rights.
Let's work out where to start
Within two weeks you get it in writing: what works, what carries risk, and a prioritized roadmap.
Request a conversation